
Phishing is a type of fraud where an attacker poses as a trusted company or person in email or other messages. Attackers often send phishing emails to spread harmful links or files that can do all kinds of damage. Crooks love this trick. It’s far easier to get you to click a bad link in a real-looking email than to break through a computer’s defenses. The more you know about phishing, the easier it is to learn how to spot and stop it.
Good phishing emails are hard to tell apart from real ones. Most claim to come from a well-known company. Some even use its logo and other details the attacker has gathered. Forget what Hollywood shows you. A hacker’s number one tool is tricking you into opening the door. Once a hacker gets into an admin account, they can wipe out a business’s digital records.
Still, a few clues can tell you a message is a phishing attempt. Watch for these:
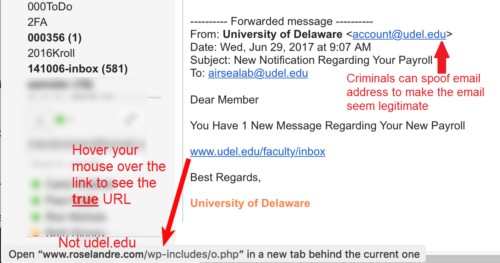
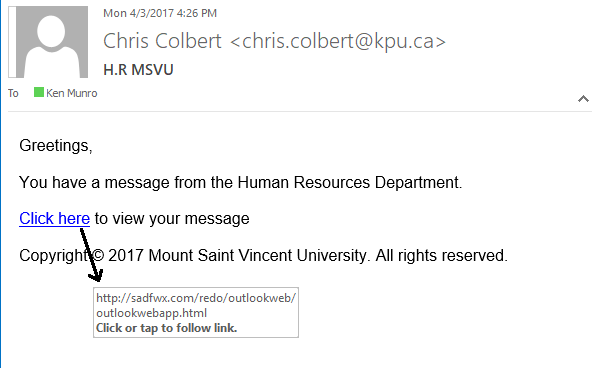
- Links use odd subdomains, misspelled URLs (typosquatting) or other strange web addresses.
- The sender uses a Gmail or other public email address instead of a corporate email address.
- It tries to scare you or rush you into acting fast.
- It asks you to confirm personal details, like bank info or a password.
- Sloppy spelling and grammar. Don’t count on this one, though. CISA warns that AI now helps scammers write emails with perfect grammar.

Phishing Emails: What To Look Out For
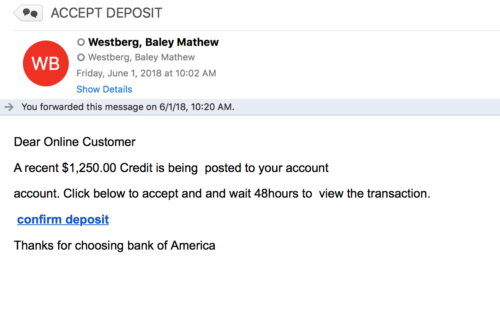
Below are a few real phishing emails and tips to keep you from falling for them. Hover your mouse over a link and check the status bar at the bottom of your window. Make sure the link goes to the right address. If you bank with Bank of America, the link should start with https://www.bankofamerica.com/ and nothing else. Fake links take you to a fake login page built to steal your password. That can hand a hacker full access and get around all your security.

Know The URL Before You Type In Credentials
Scammers send lots of spam to email addresses tied to a website. Some of these phishing emails just want your login. They get you to click a link that opens a fake login page. So know your website’s login URL. A URL is a web page’s address, shown in the address bar at the top of your browser.
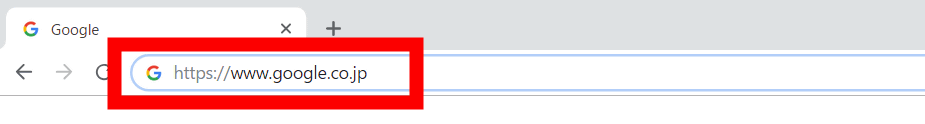
If your website is WordPress, type yourdomain.com/wp-admin to reach your login. Your real login lives at the URL yourdomain.com/wp-login.php. It may have a ? followed by what looks like random words and numbers, like this: https://sedo.com/us/services/broker-service/?tracked=&partnerid=&language=us. The part after the ? holds arguments, which are just internal notes the site uses. What matters is the yourdomain.com/wp-login.php part. The address must start with it. If it starts with someotherdomain.something/something, it’s fake and dangerous.
This rule applies everywhere! Say an email claims to come from a company and a link asks you to log in. The URL should start with companydomain.something/something or maybe something.companydomain.something/something. Let’s say “Google” emails you about a problem and asks you to click. If the login page URL reads something.google.com/something, it’s real. If it reads fgdfy.gobble.cz/login, it’s clearly fake.
A Quick Phishing Emails Checklist
Most phishing emails fail at least one of these checks. Run through them before you click, reply or pay anything.
- Does the sender’s address match the company’s real domain, letter for letter?
- Does the link go where it claims? Hover first, or type the address yourself.
- Is it pushing you to act right now or face a penalty?
- Does it ask for a password, a code, bank details or a gift card?
- Did you expect this attachment or invoice?
- Would this person normally contact you this way?
If a message still looks real, don’t use its links. CISA advises checking with the company through its official website or a phone number you already trust.
What To Do If You Clicked
Mistakes happen, even to careful people. What matters is how fast you act. Here’s the order we walk clients through:
- Don’t enter anything else. Close the page right away.
- Change the password you typed in. Do it from a different, trusted device. A password manager makes that change quick and keeps each login unique.
- Turn on multi-factor login for that account if it isn’t on already.
- Tell whoever handles your IT, so they can check for other logins.
- If you shared bank or card details, call your bank right away.
- If you opened a file, update your security software and run a full scan.
The FTC says to visit IdentityTheft.gov if scammers got your personal details. That site builds a recovery plan for your exact case.
Report It
Reporting helps shut scams down faster. Forward phishing emails to reportphishing@apwg.org, and forward scam texts to 7726 (SPAM). You can also file a report at ReportFraud.ftc.gov. If your business lost money, file with the FBI at IC3.gov too.
Protect Your Whole Team
This isn’t a rare problem. The FBI’s 2025 Internet Crime Report logged over one million complaints and nearly $21 billion in losses. Phishing and spoofing ranked among the three most reported crime types.
Training helps your staff spot phishing emails, but a few settings protect everyone at once:
- Multi-factor login: a stolen password alone won’t get a crook in.
- Email authentication: SPF, DKIM and DMARC make it harder to fake mail from your domain.
- Backups: a clean copy of your files lets you recover without paying anyone.
- Updates: keep phones, computers and security tools current.
The FTC explains email authentication in plain terms. If you’re not sure how to set it up, your email host can do it. If they won’t, the FTC suggests finding a host that will.
How We Set This Up for Small Offices
When we lock down email for a small team, we start with the domain records. We check that SPF, DKIM and DMARC exist and actually pass. Next, we turn on multi-factor login for every mailbox, starting with the owner and anyone who pays bills. Finally, we show staff how to report a suspect message with one click. A DNS filter like Pi-hole can also block many known phishing domains. Pair that with a secure guest Wi-Fi setup, and you close two of the most common doors.
Owners here in Southwest Florida often run lean teams, and one person may handle email, billing and payroll. That makes a single fake invoice far more dangerous. Build in a simple rule: any change to payment details gets confirmed by phone.
Train Your Team to Spot Phishing
Want your team to spot phishing before it costs you? Contact us and we’ll talk through your options.
Phishing Emails FAQ
Opening a message on an updated device is usually low risk. The real danger comes from clicking links, opening attachments or replying with details.
Don’t click or reply. Use your inbox’s report button, forward it to reportphishing@apwg.org, then delete it.
No. Filters catch a lot, but well-made scams still slip through. Your team’s habits are the last line of defense.
Yes. The same tricks show up in texts, calls and social media messages. Use the same checks, and forward scam texts to 7726.
 Call Now